01
Offensive Testing
Comprehensive offensive security testing and vulnerability assessment
OFFENSIVE SECURITY · DEFENSIVE IMPACT
Hi, I’m Sheet Abdullah.
Security Researcher & Bug Bounty Hunter
Discovering vulnerabilities before malicious actors do. Focused on offensive security, penetration testing, and research that makes the digital world safer.
01 / ABOUT ME
“Finding vulnerabilities is not about breaking things — it’s about building more secure systems.”
I’m a dedicated Cybersecurity Researcher and Bug Bounty Hunter with extensive expertise in offensive security testing.
My journey has been shaped by industry-recognized certifications including OSCP+, OSWE, OSEP, OSCP, OSWP, OSIR, OSTH, OSWA, eCPPT, eWPTX, eMAPT, CRTA, and CAPT.
My expertise spans web application security, mobile penetration testing, cloud security assessments, network infrastructure testing, and red team operations.
With hands-on experience in penetration testing, vulnerability management, digital forensics, and OSINT, I help organizations strengthen their security posture through bug bounty programs on HackerOne and Bugcrowd, and professional security consulting.
Explore my background ↗02 / SKILLS & SERVICES
From applications to infrastructure, practical security expertise across the stack.
Comprehensive offensive security testing and vulnerability assessment
Full-stack web application security testing and penetration testing
iOS and Android application security testing and reverse engineering
Cloud infrastructure security assessment and hardening
Network security assessment and infrastructure penetration testing
Red team exercises and adversary simulation
Cybersecurity training and educational workshops
Security consultation and advisory services
03 / CERTIFICATIONS & ACHIEVEMENTS
Professional credentials across offensive security, application testing, and security foundations.
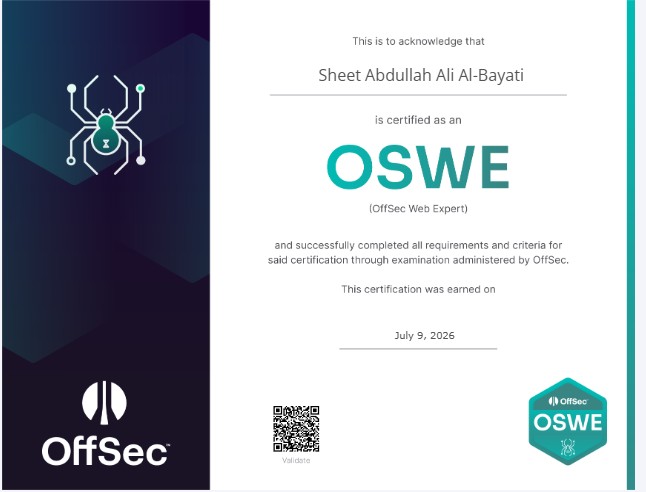 View certificate ↗
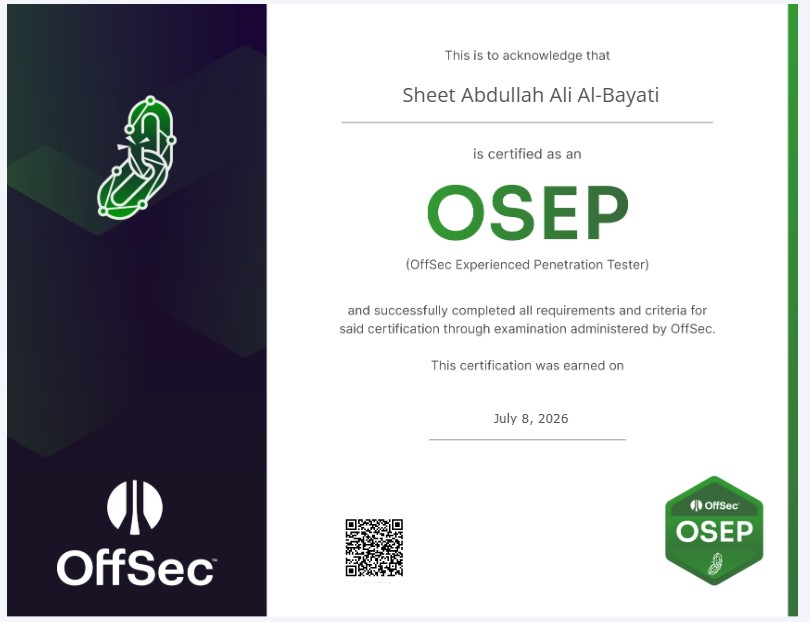 View certificate ↗
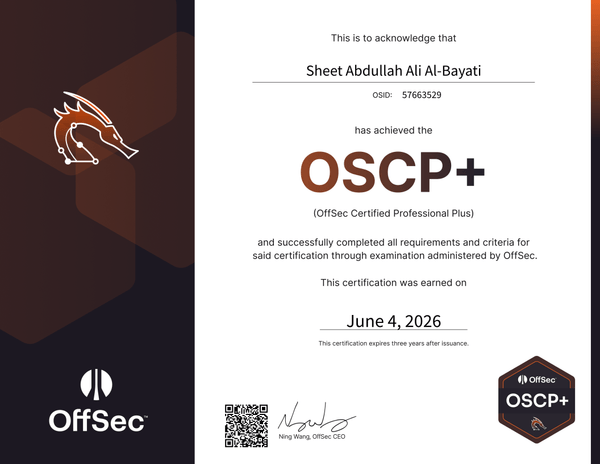 View certificate ↗
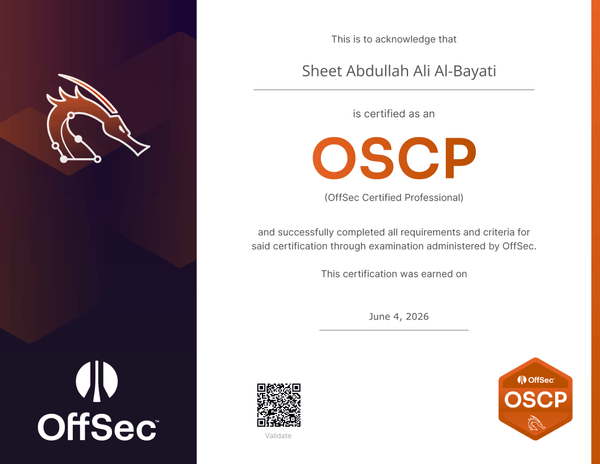 View certificate ↗
 View certificate ↗
 View certificate ↗
 View certificate ↗
 View certificate ↗
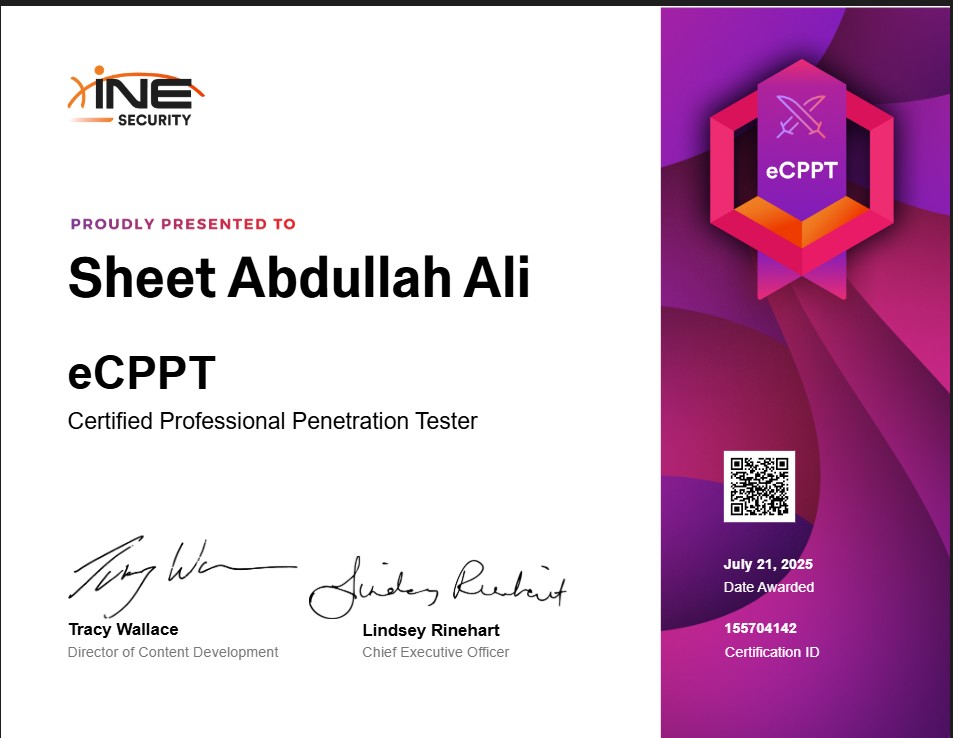 View certificate ↗
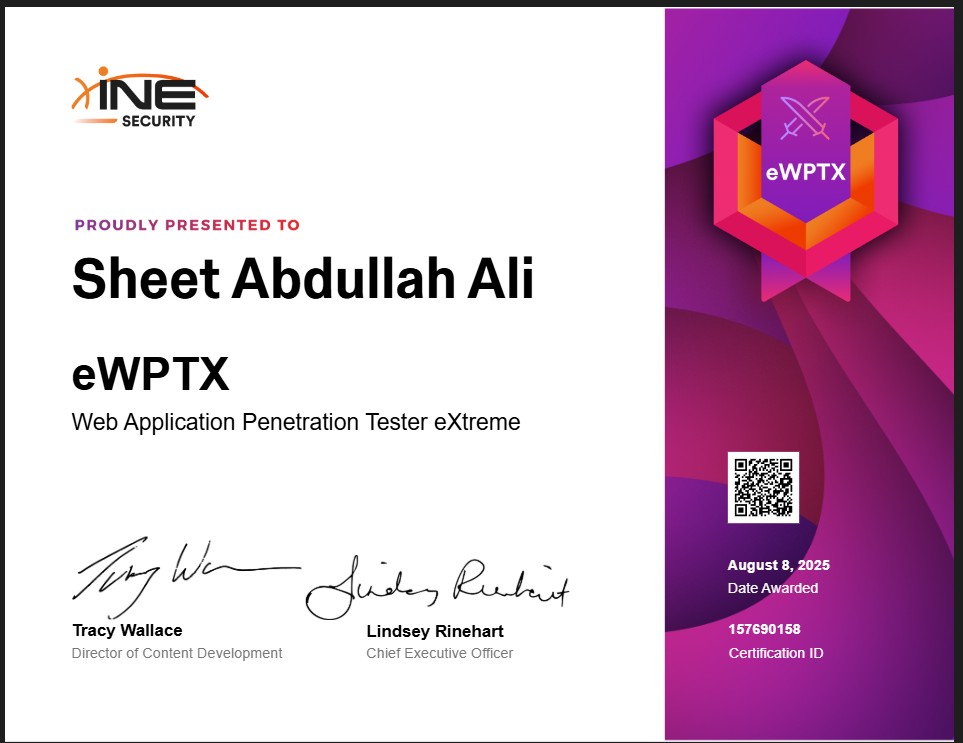 View certificate ↗
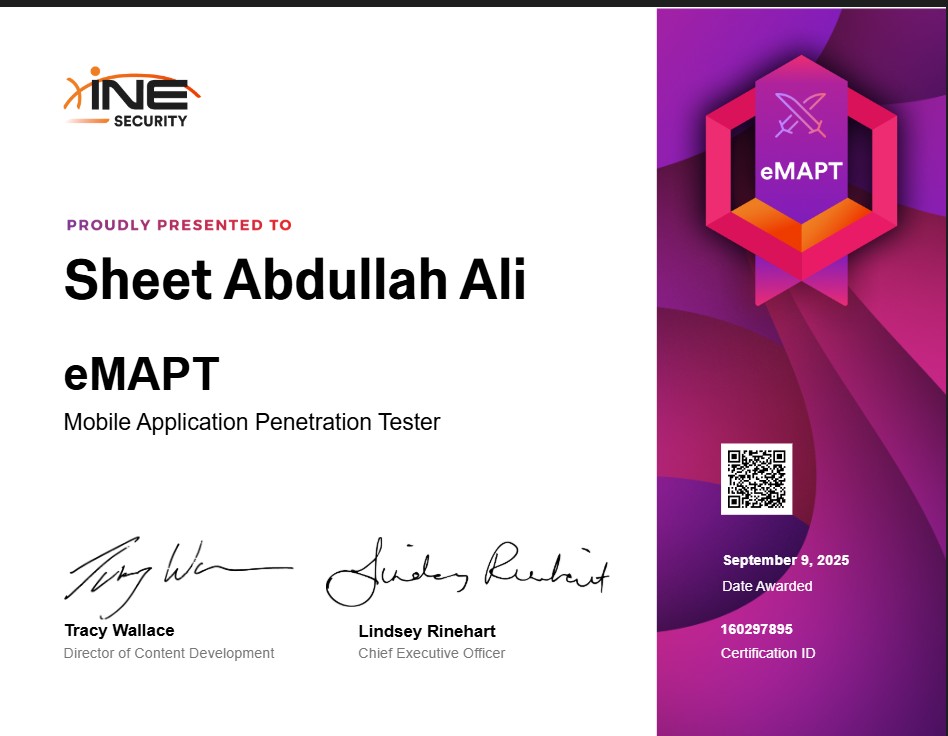 View certificate ↗
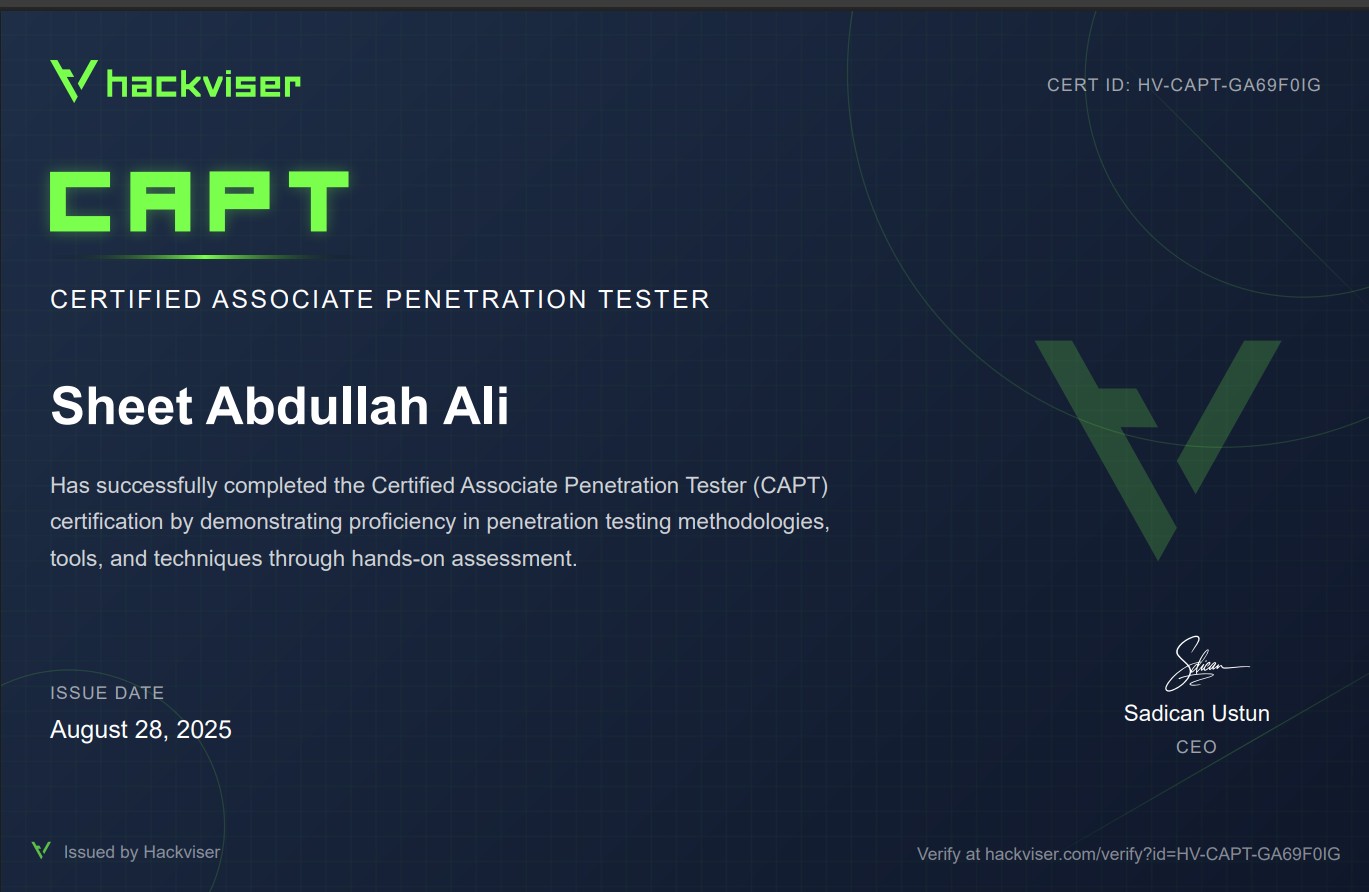 View certificate ↗
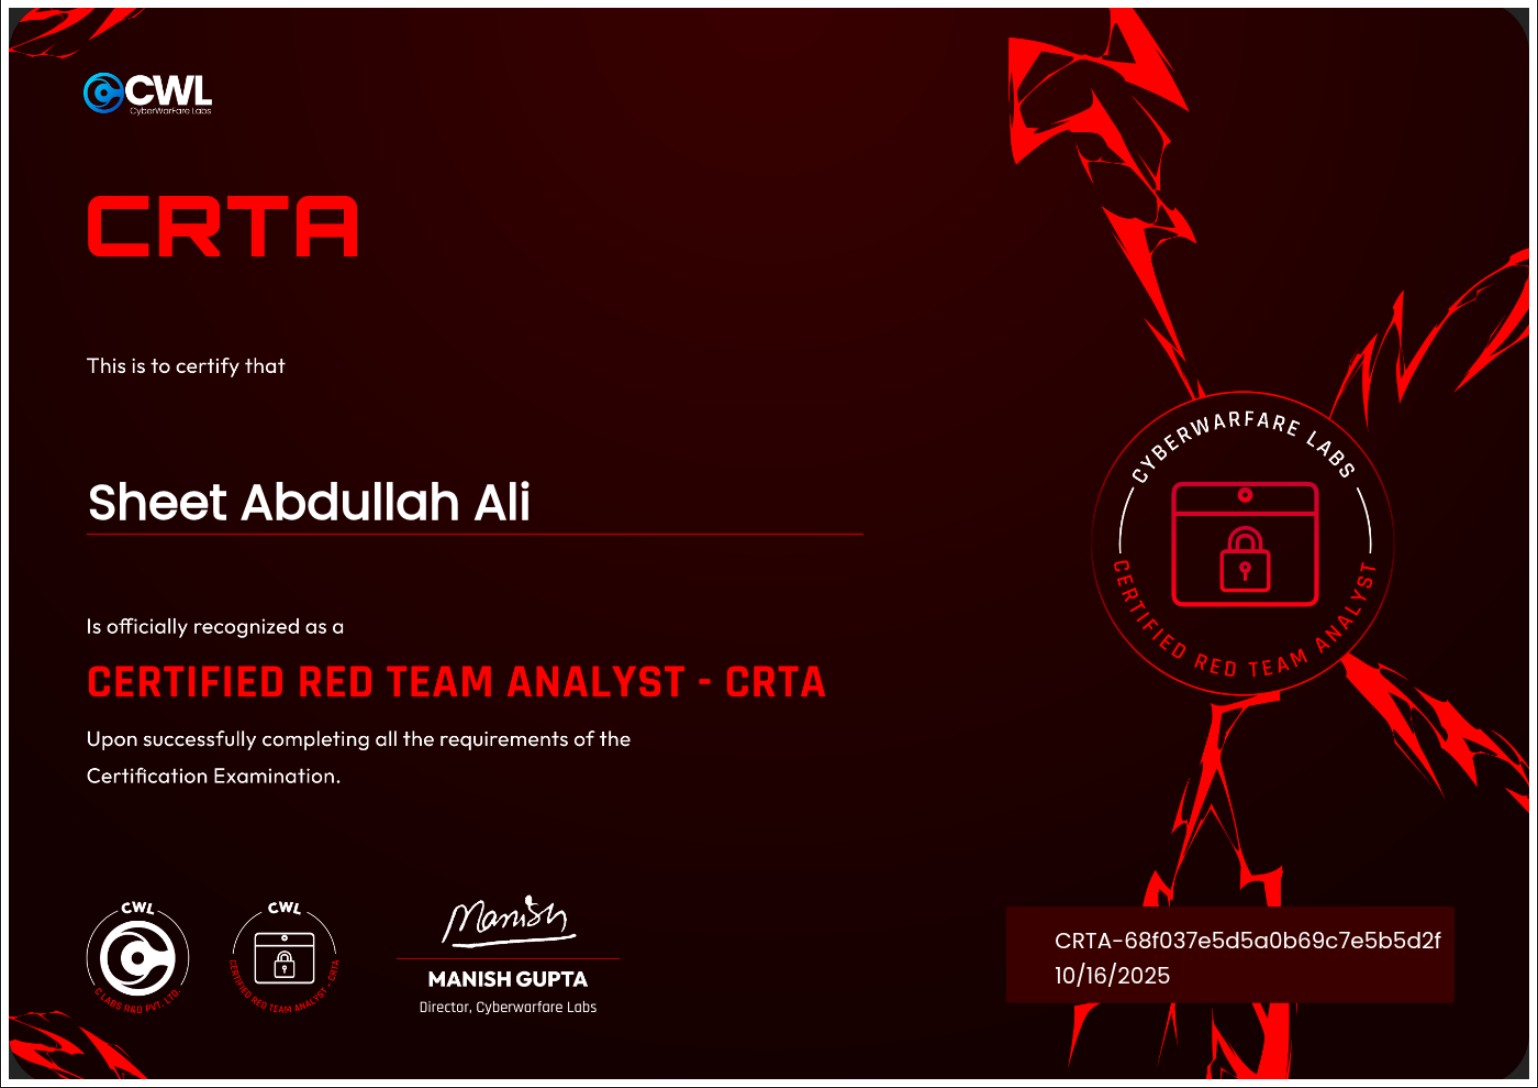 View certificate ↗
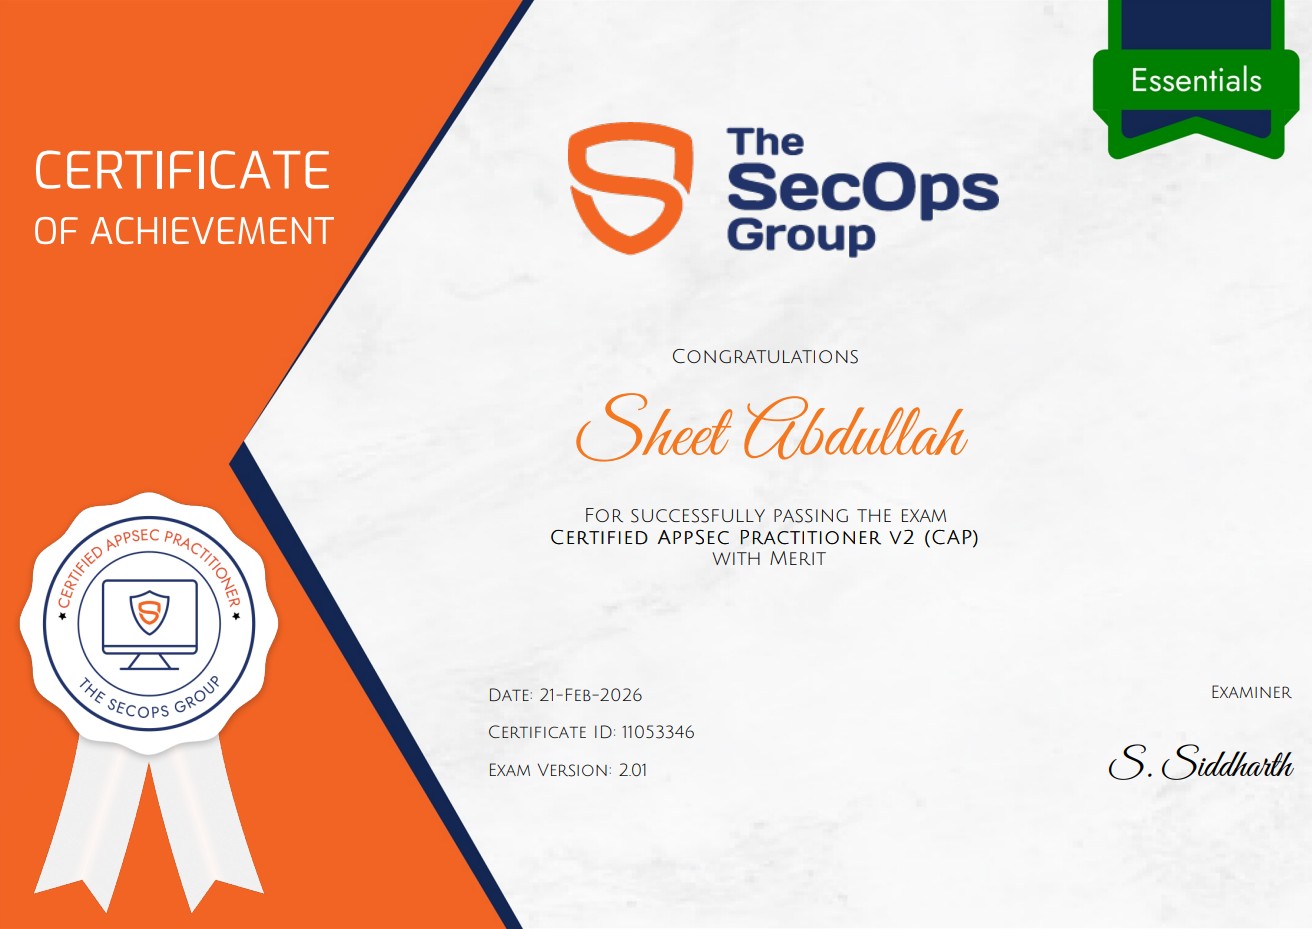 View certificate ↗
Certified AppSec Practitioner V2
ID: 11053346
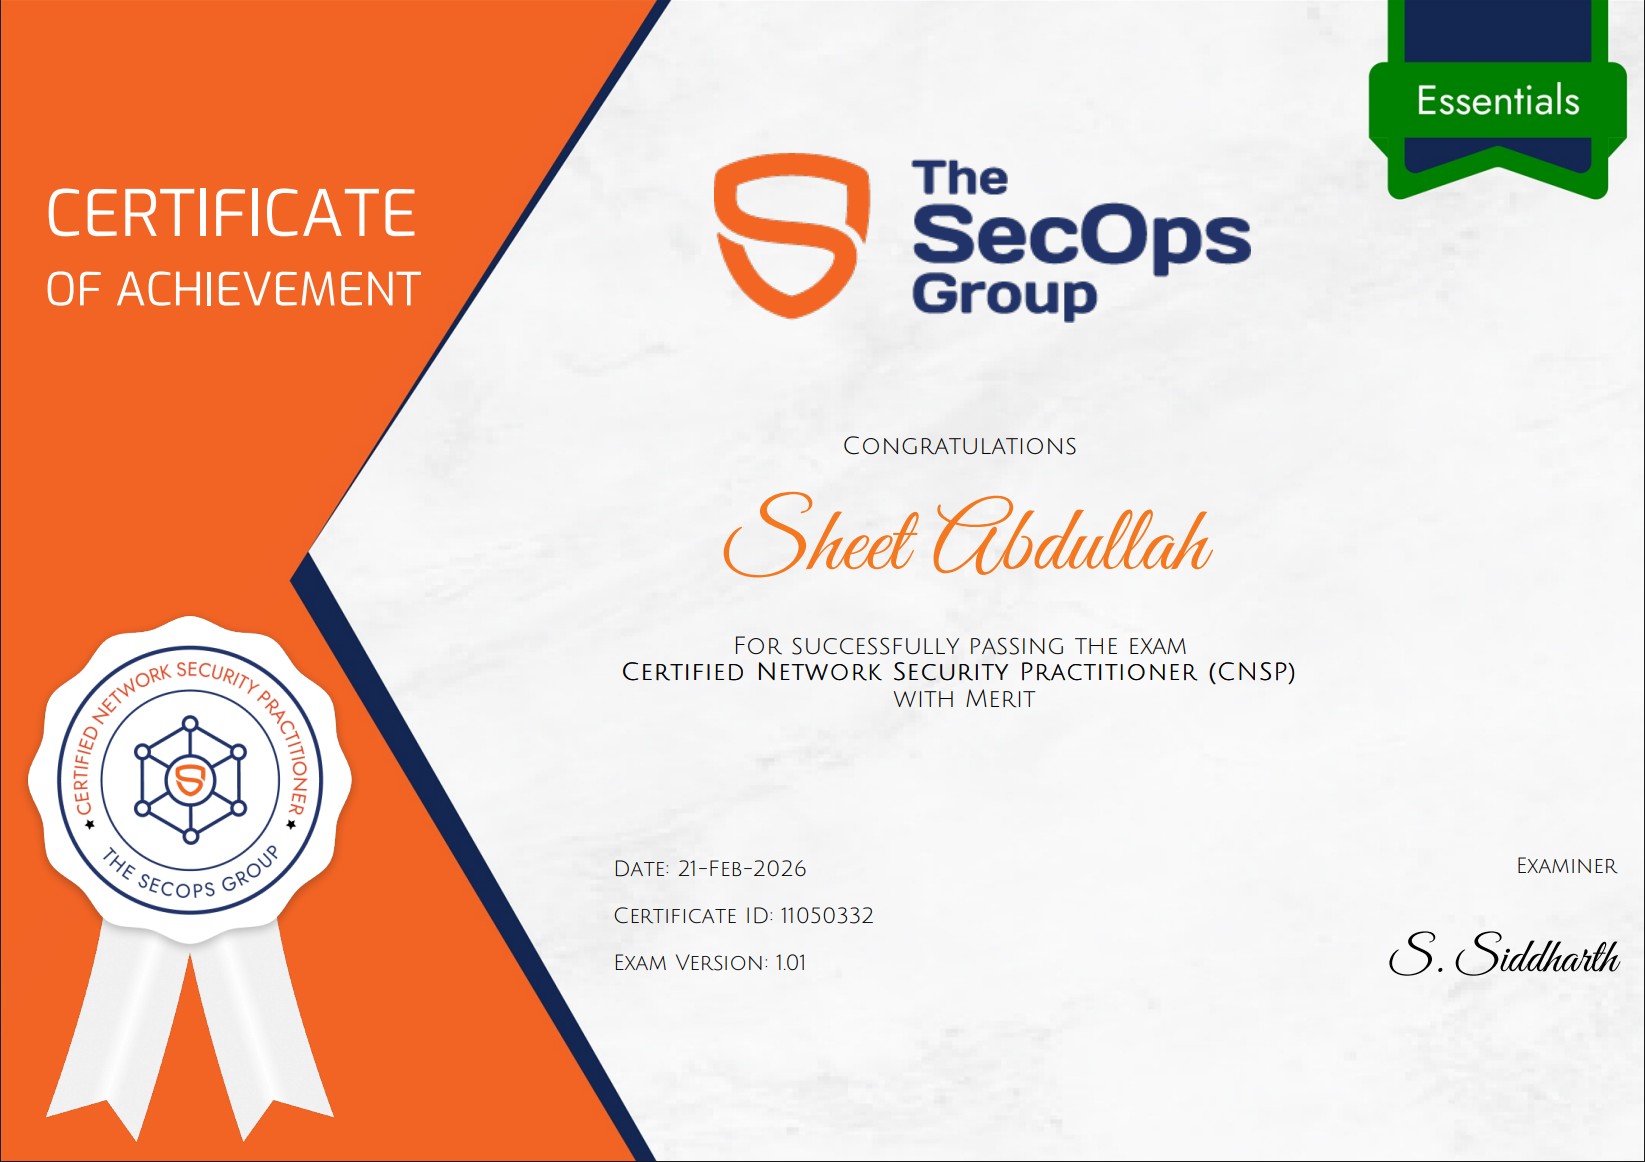 View certificate ↗
Certified Network Security Practitioner
ID: 11050332
 View certificate ↗
04 / SECURITY RESEARCH
Vulnerability research, technical articles, and insights from the offensive side.
Explore the existing research summaries, covering web vulnerabilities, API security, and mobile reverse engineering.
All research & write-ups ↗Discovered a stored XSS vulnerability affecting 50M+ users. Full technical breakdown and exploitation chain.
Automated methodology for discovering subdomain takeover vulnerabilities across large infrastructure.
Chaining multiple IDOR vulnerabilities to achieve full account takeover. Step-by-step analysis.
Exploiting a race condition to duplicate payment transactions. $10,000 bounty awarded.
Comprehensive guide to securing REST APIs and common vulnerability patterns to avoid.
Deep dive into Android app security: from decompilation to discovering hidden endpoints.
05 / PROJECTS & PRACTICE
CODE & AUTOMATION
Find my repositories and follow my work on GitHub. My toolkit includes custom Python and Bash automation scripts.
Visit GitHubBUG BOUNTY
Connect with my bug bounty work through my existing researcher profiles.
06 / CONTACT
Have a security assessment in mind, a research collaboration, or a question? Let’s start a conversation.
sheet.cyber@gmail.comFIND ME ELSEWHERE
Prefer a direct conversation? Email or reach out on LinkedIn anytime.